PHI exposure detection for healthcare teams

Find patient-data exposures.

Show how you responded.

Compliance Doctor flags patient data that leaves your approved systems and logs every response with its evidence, so you stay audit-ready.

No patient data needed for the demo.

Built by Time Doctor, used by 10,000+ distributed teams

The risk

Would you know if your staff did this?

Policies set the rules, and your EHR audit log tracks access inside the EHR. Neither shows where patient data goes once it leaves.

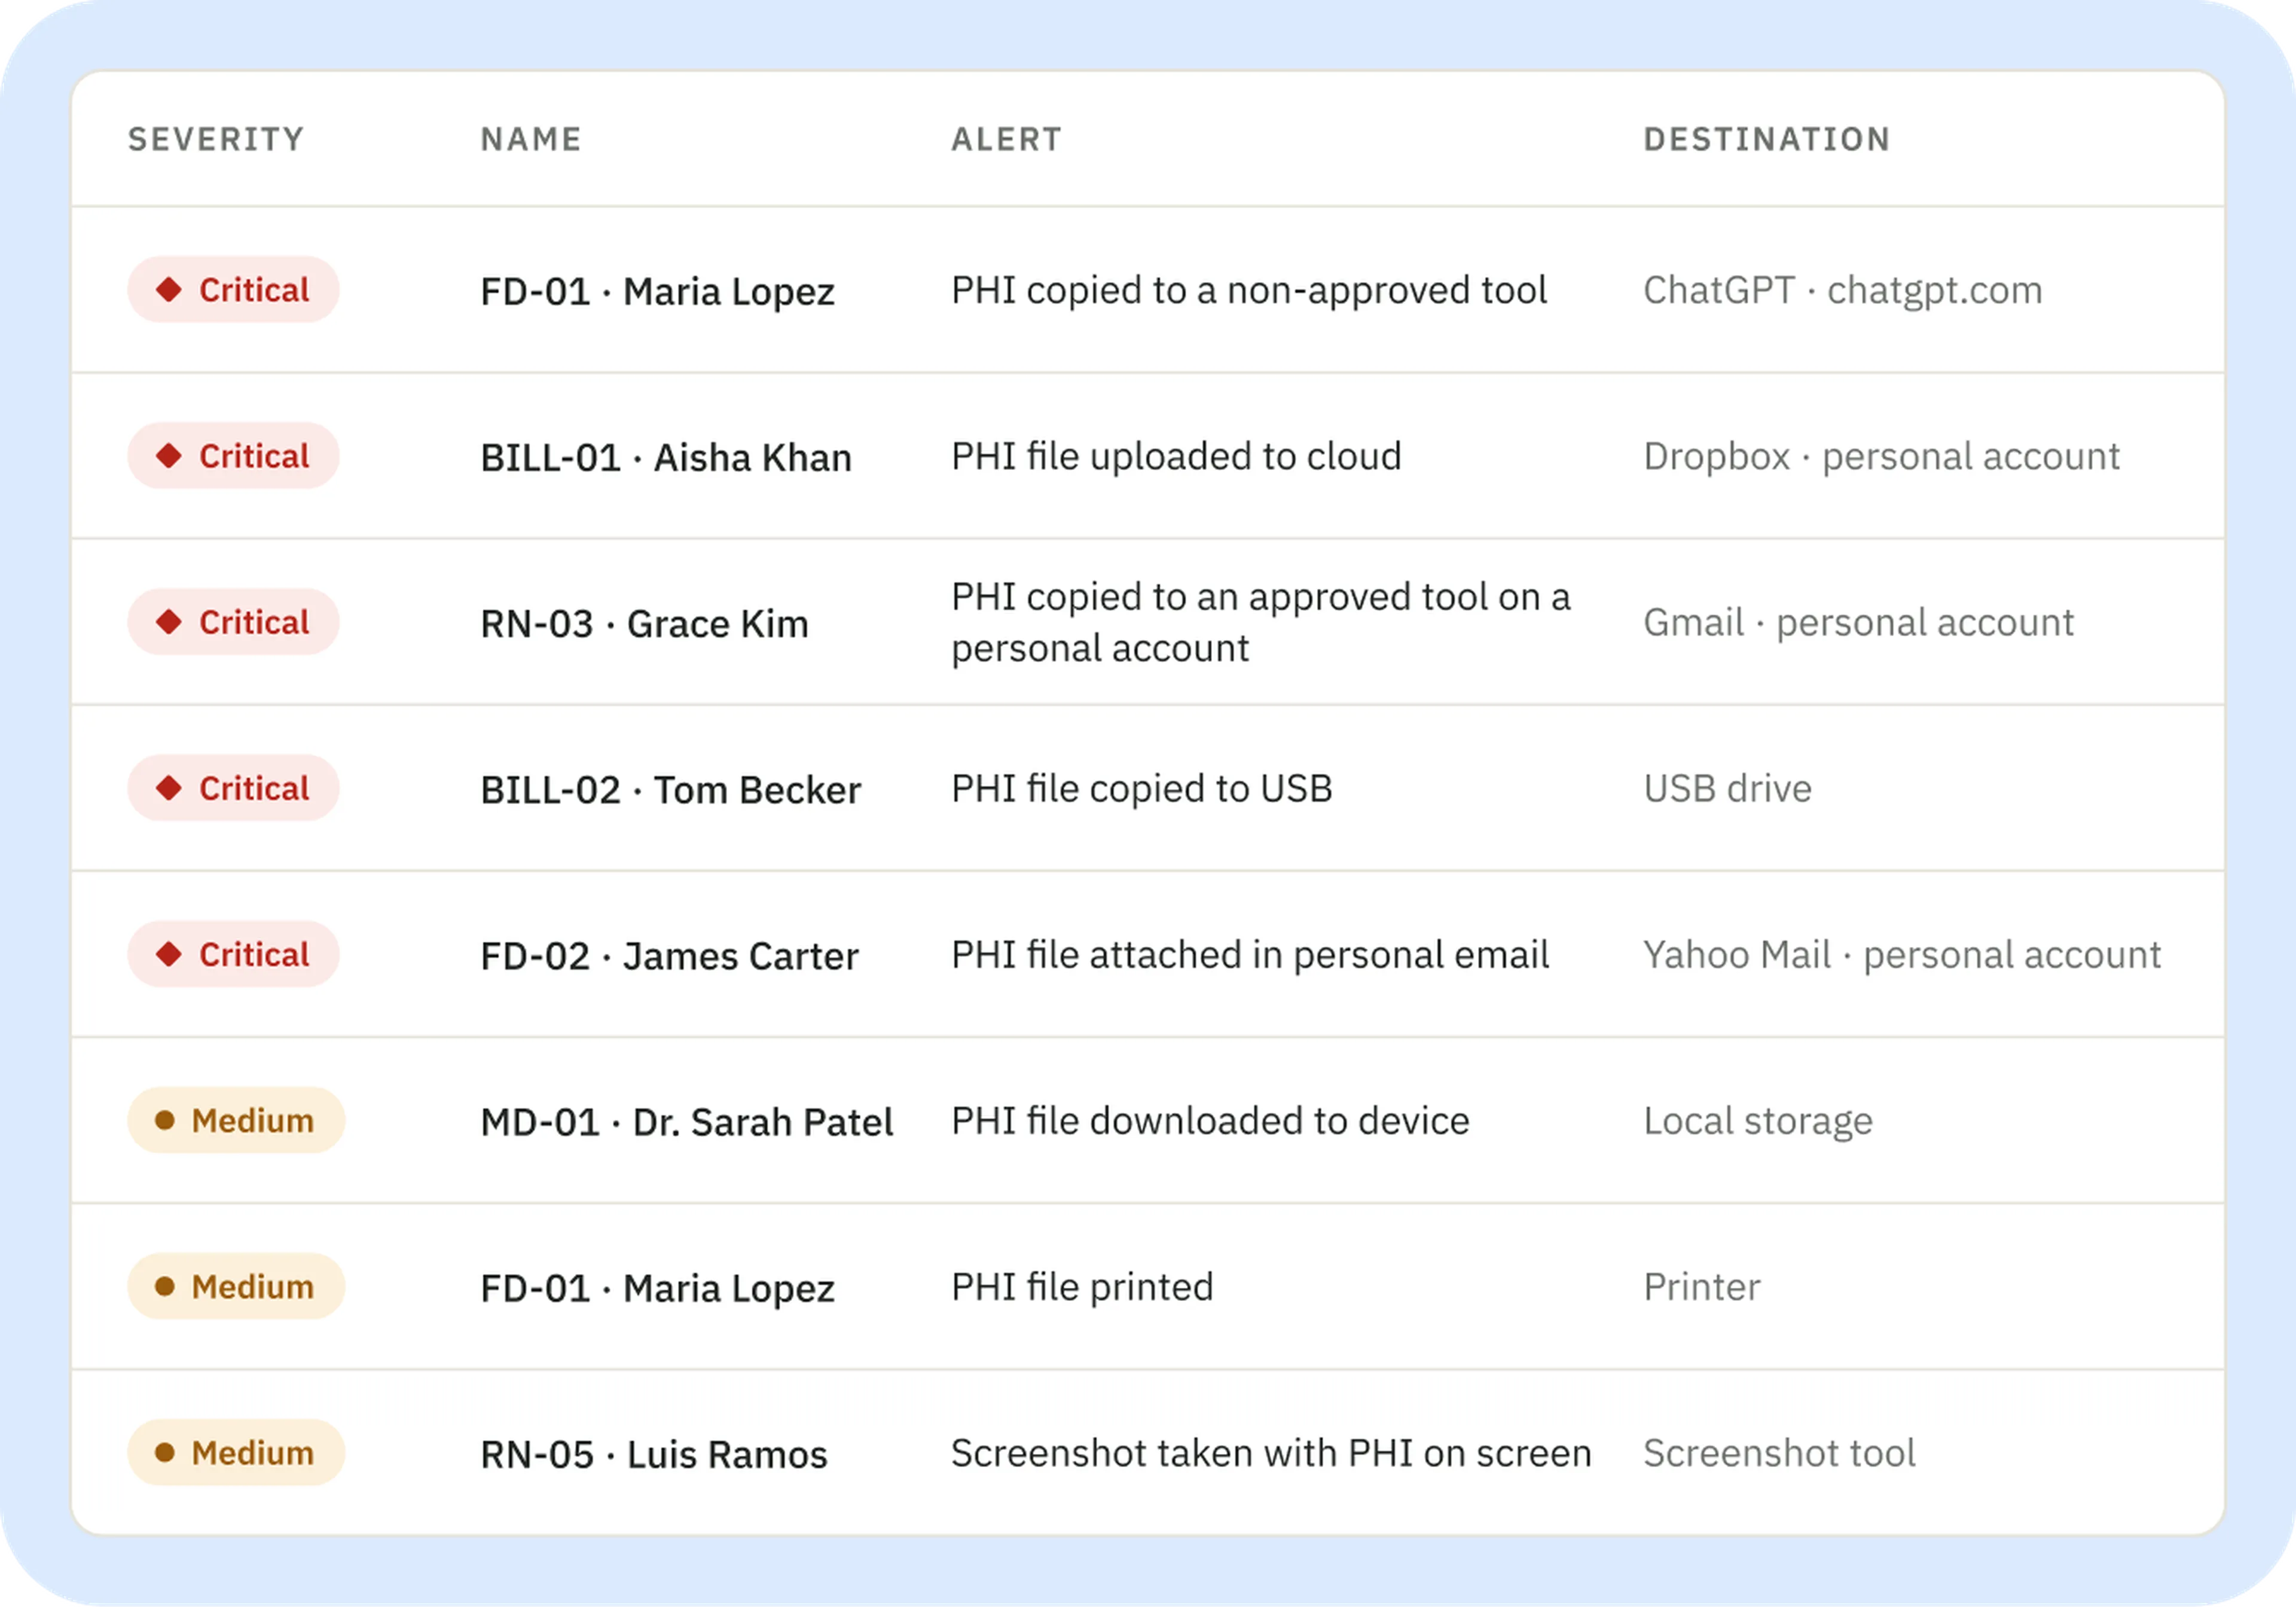
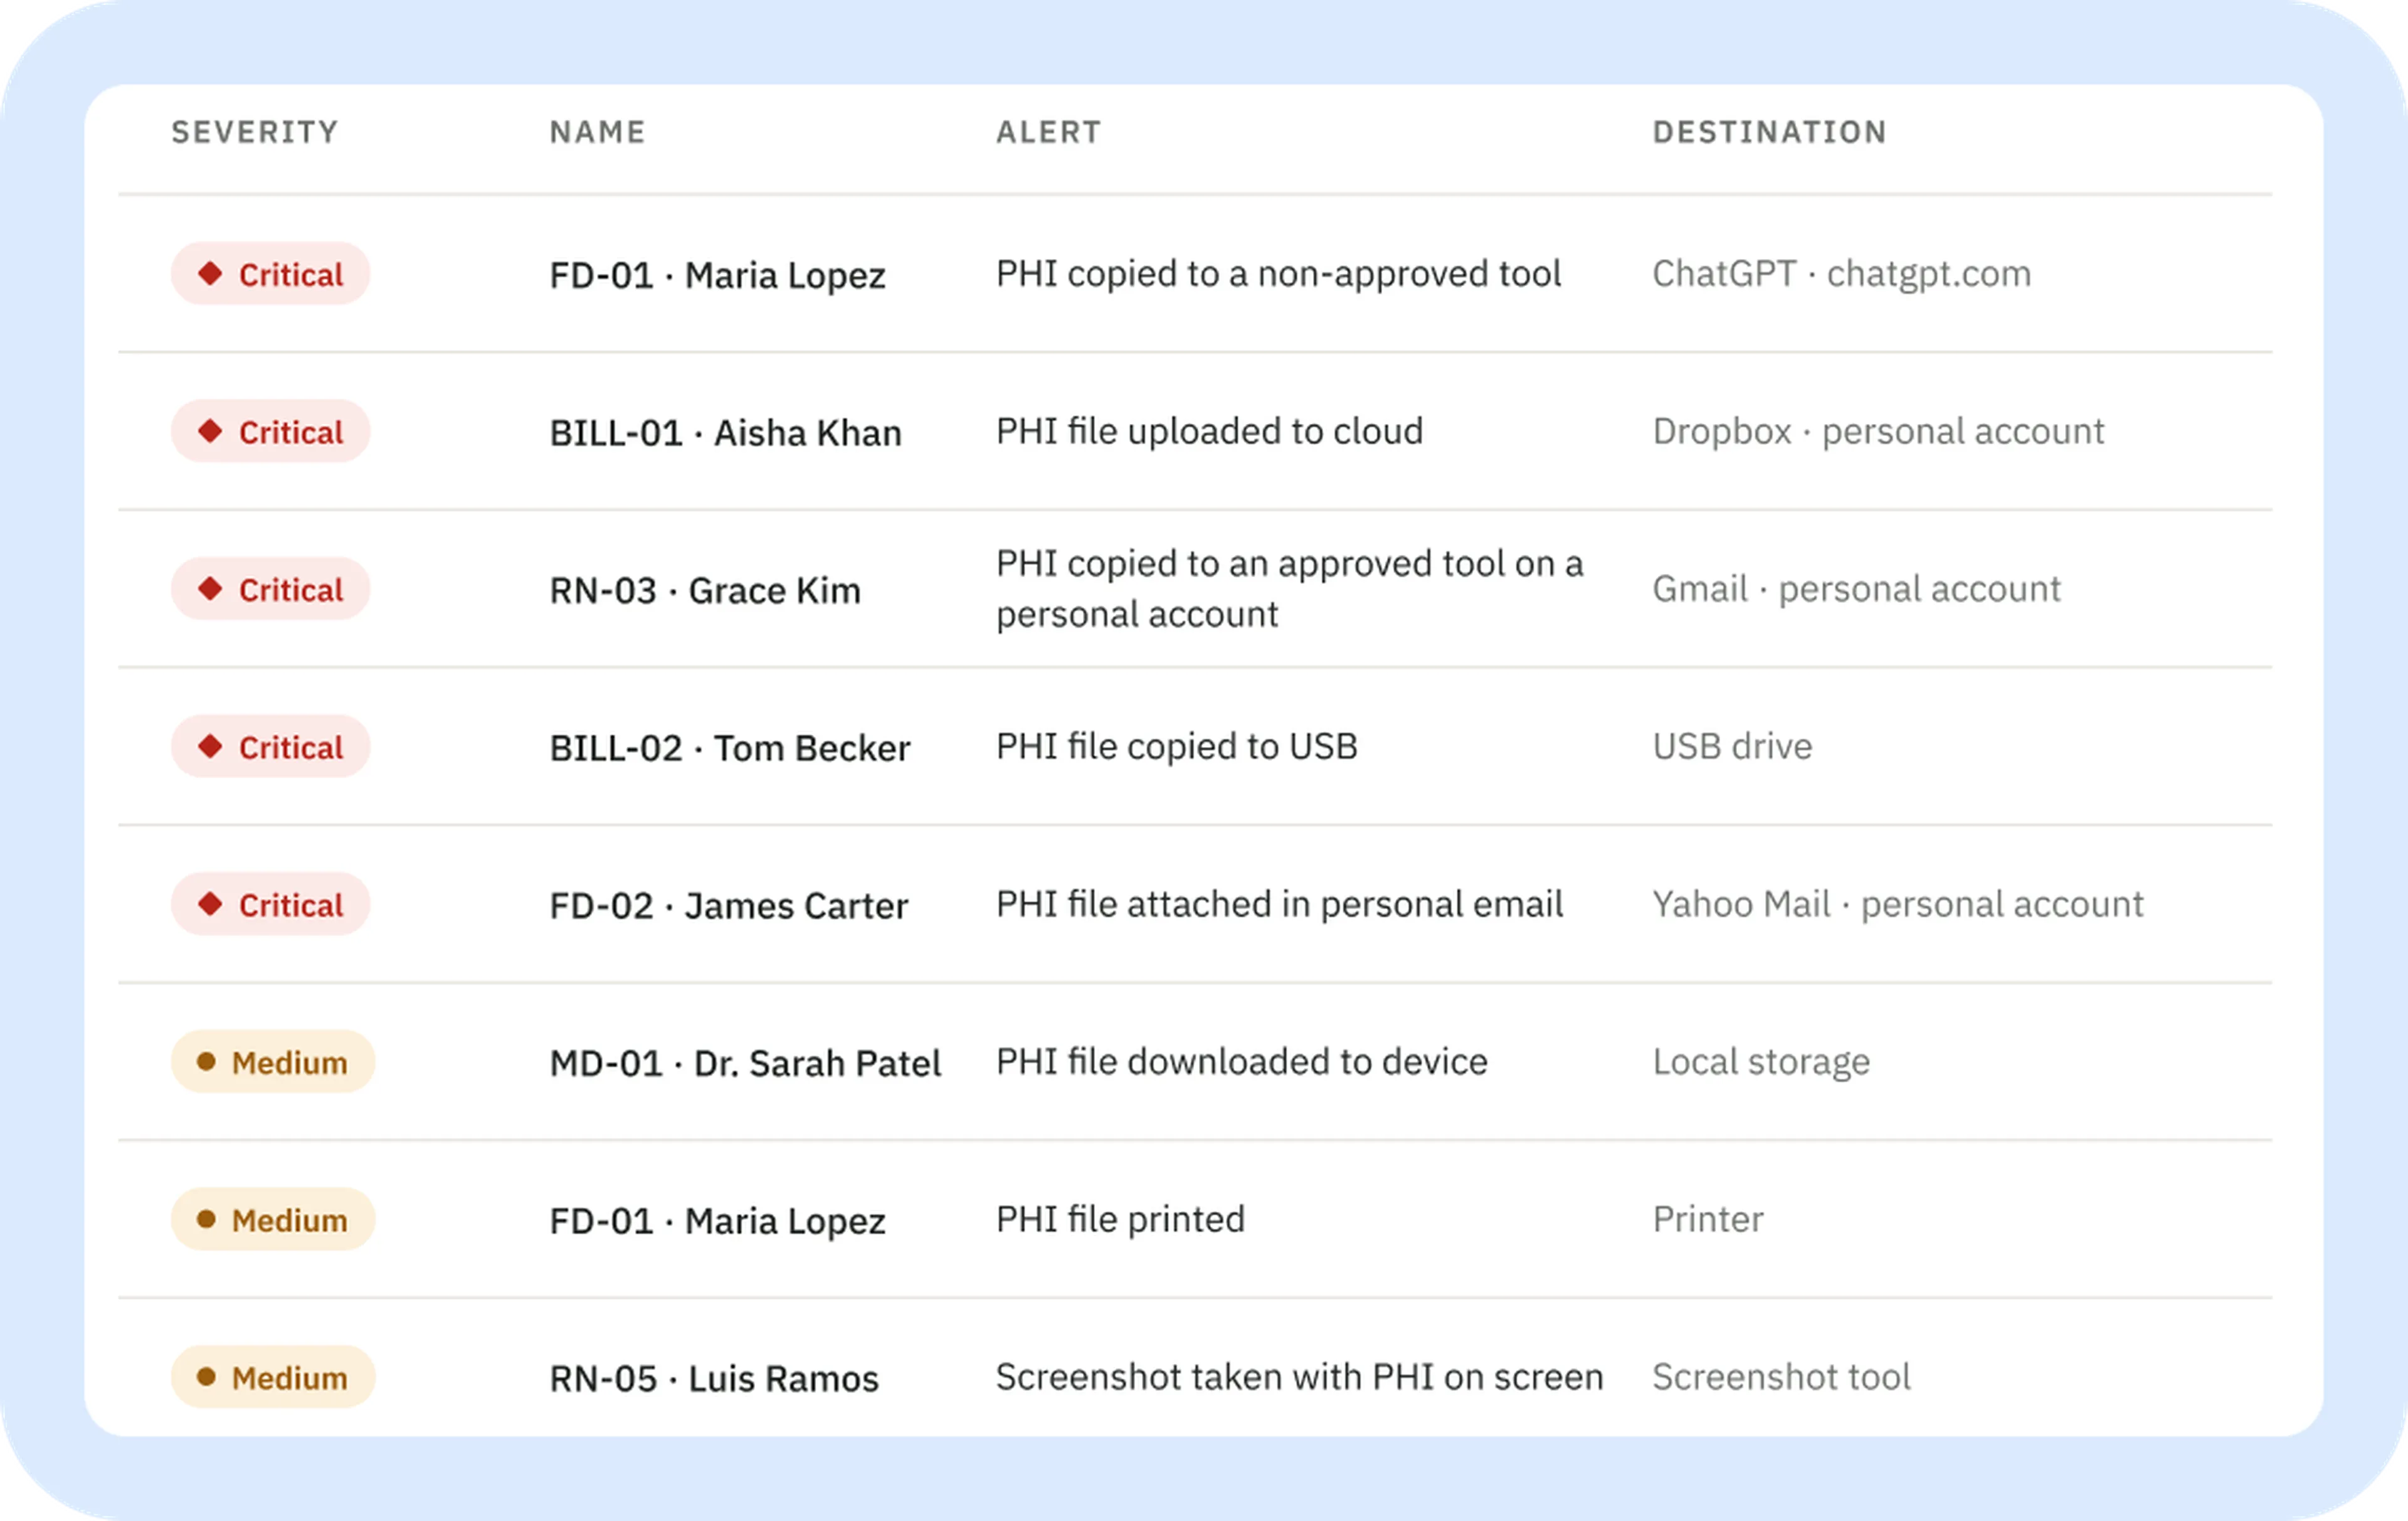
A discharge summary pasted into an AI app

Patient data copied to a personal Gmail account

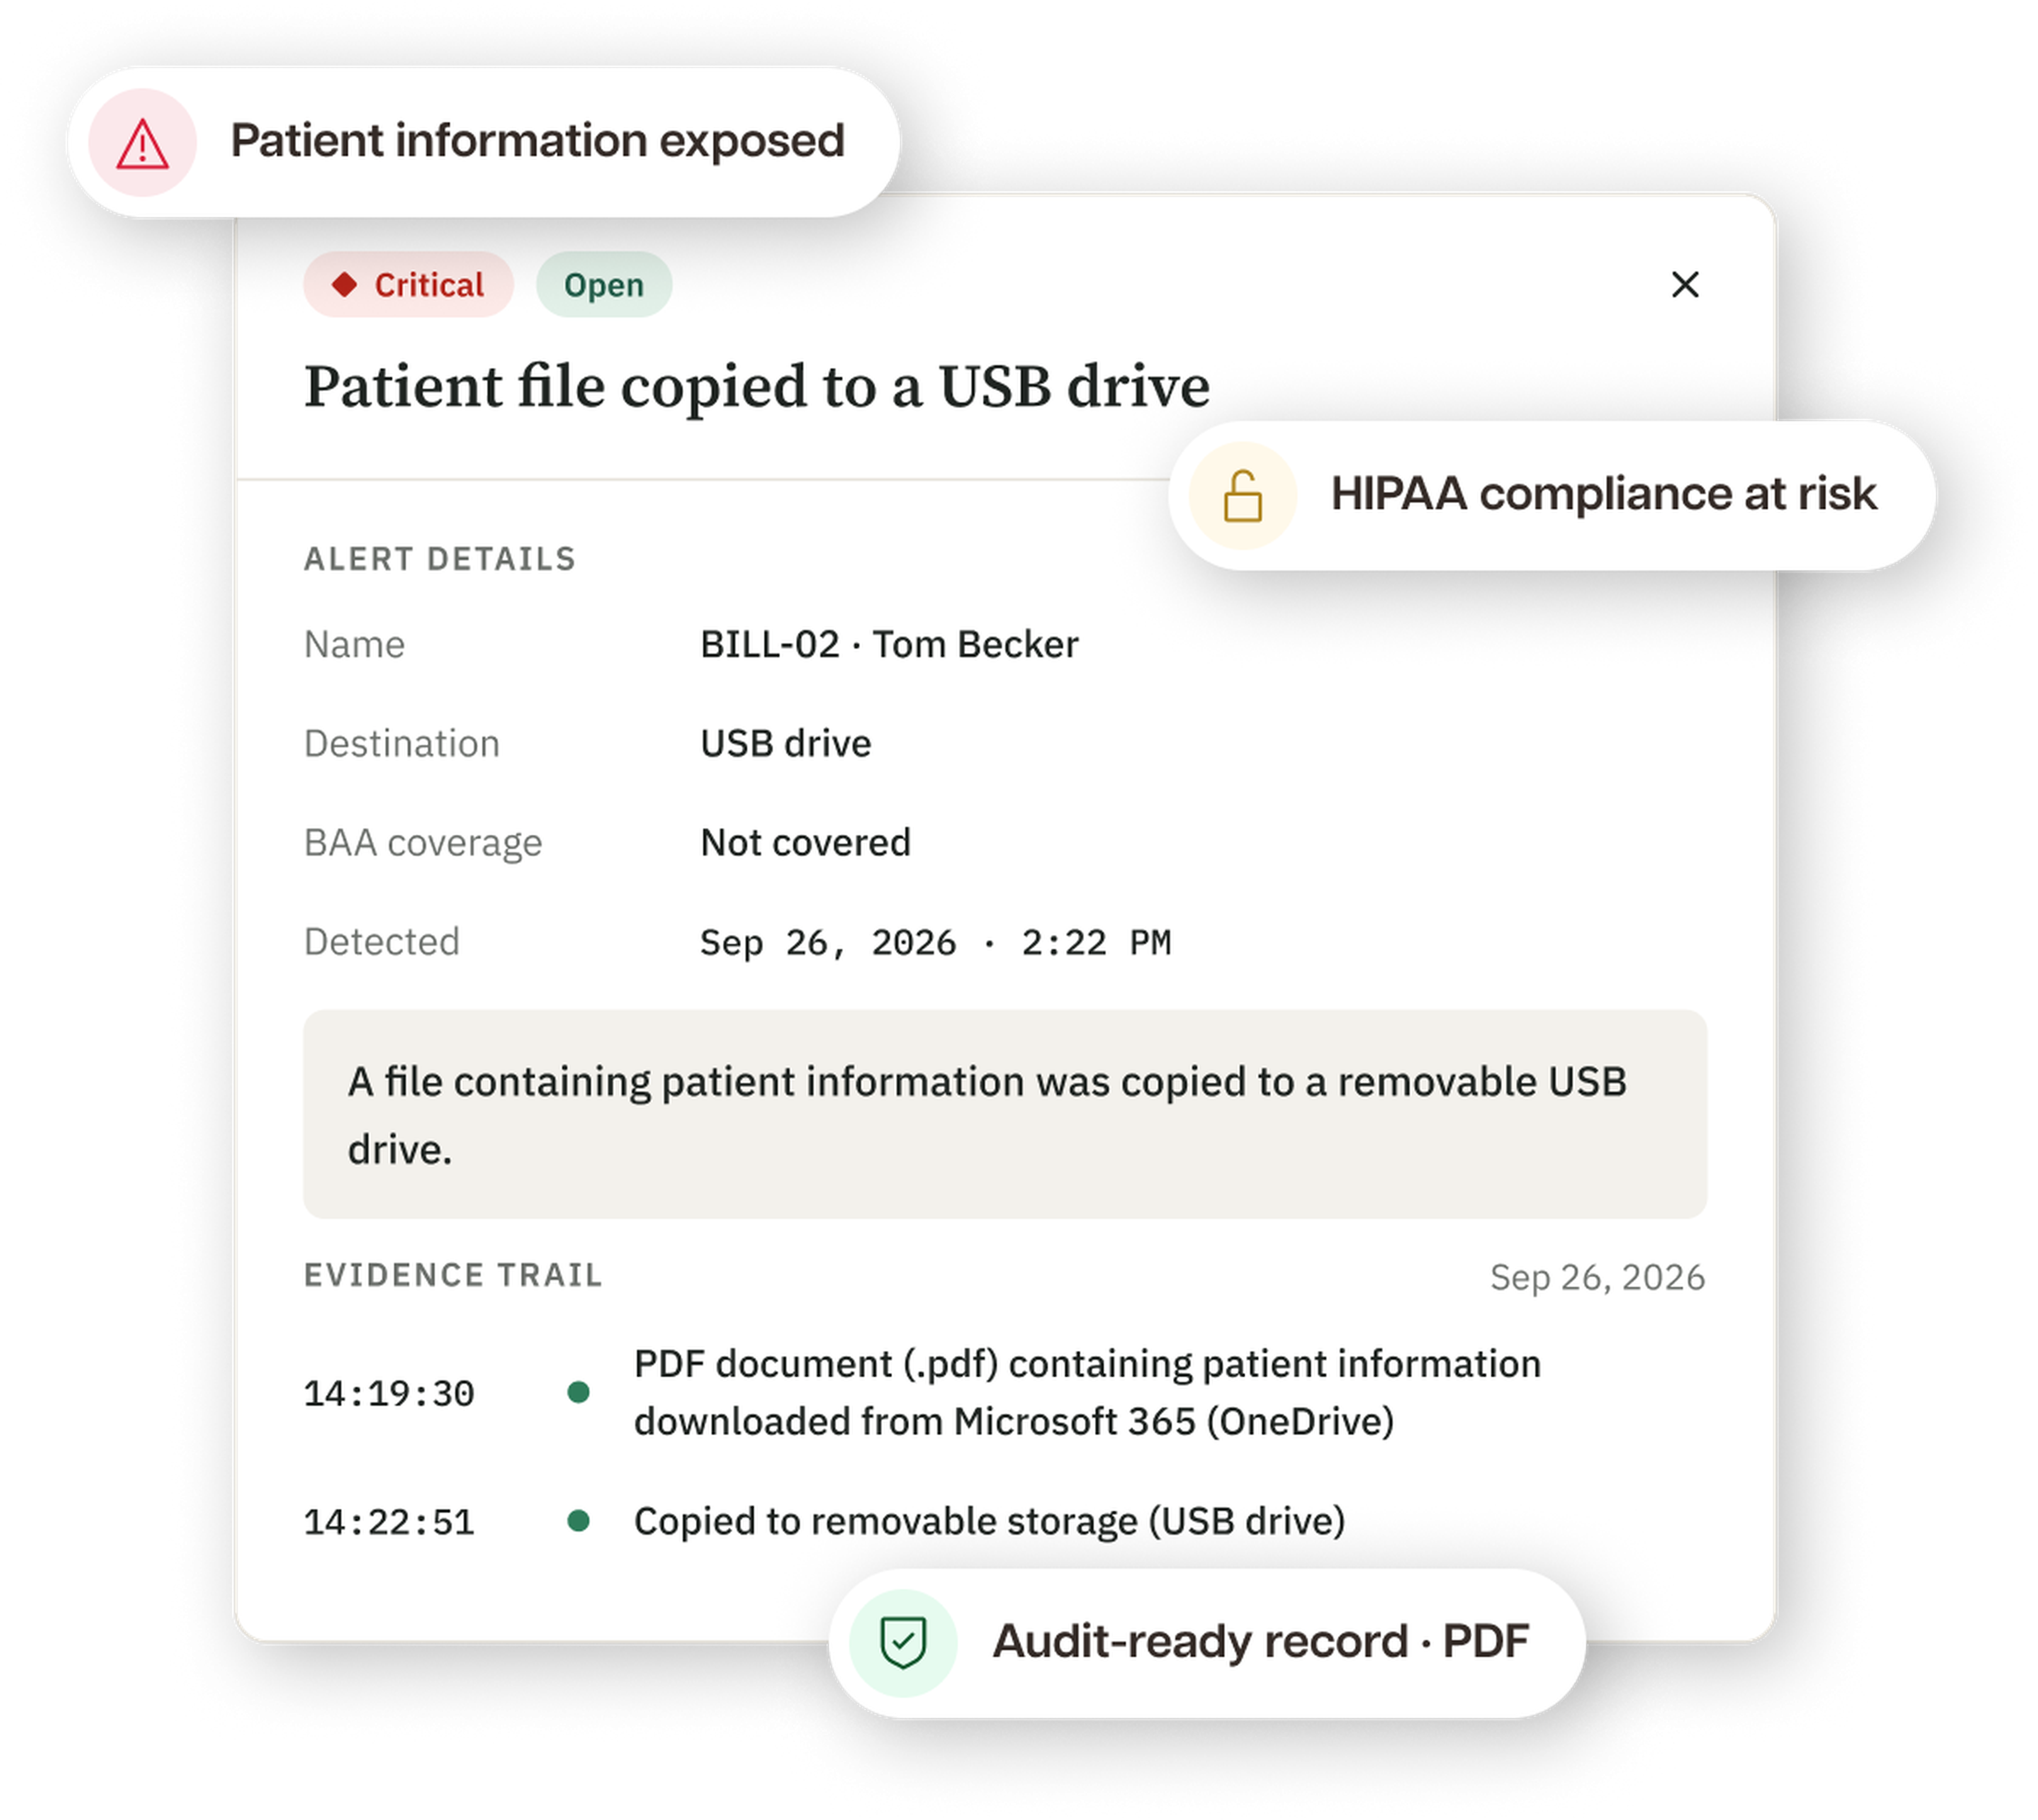
A patient file copied to a USB drive

A patient file uploaded to personal cloud storage

How it works

From exposure to evidence in three steps

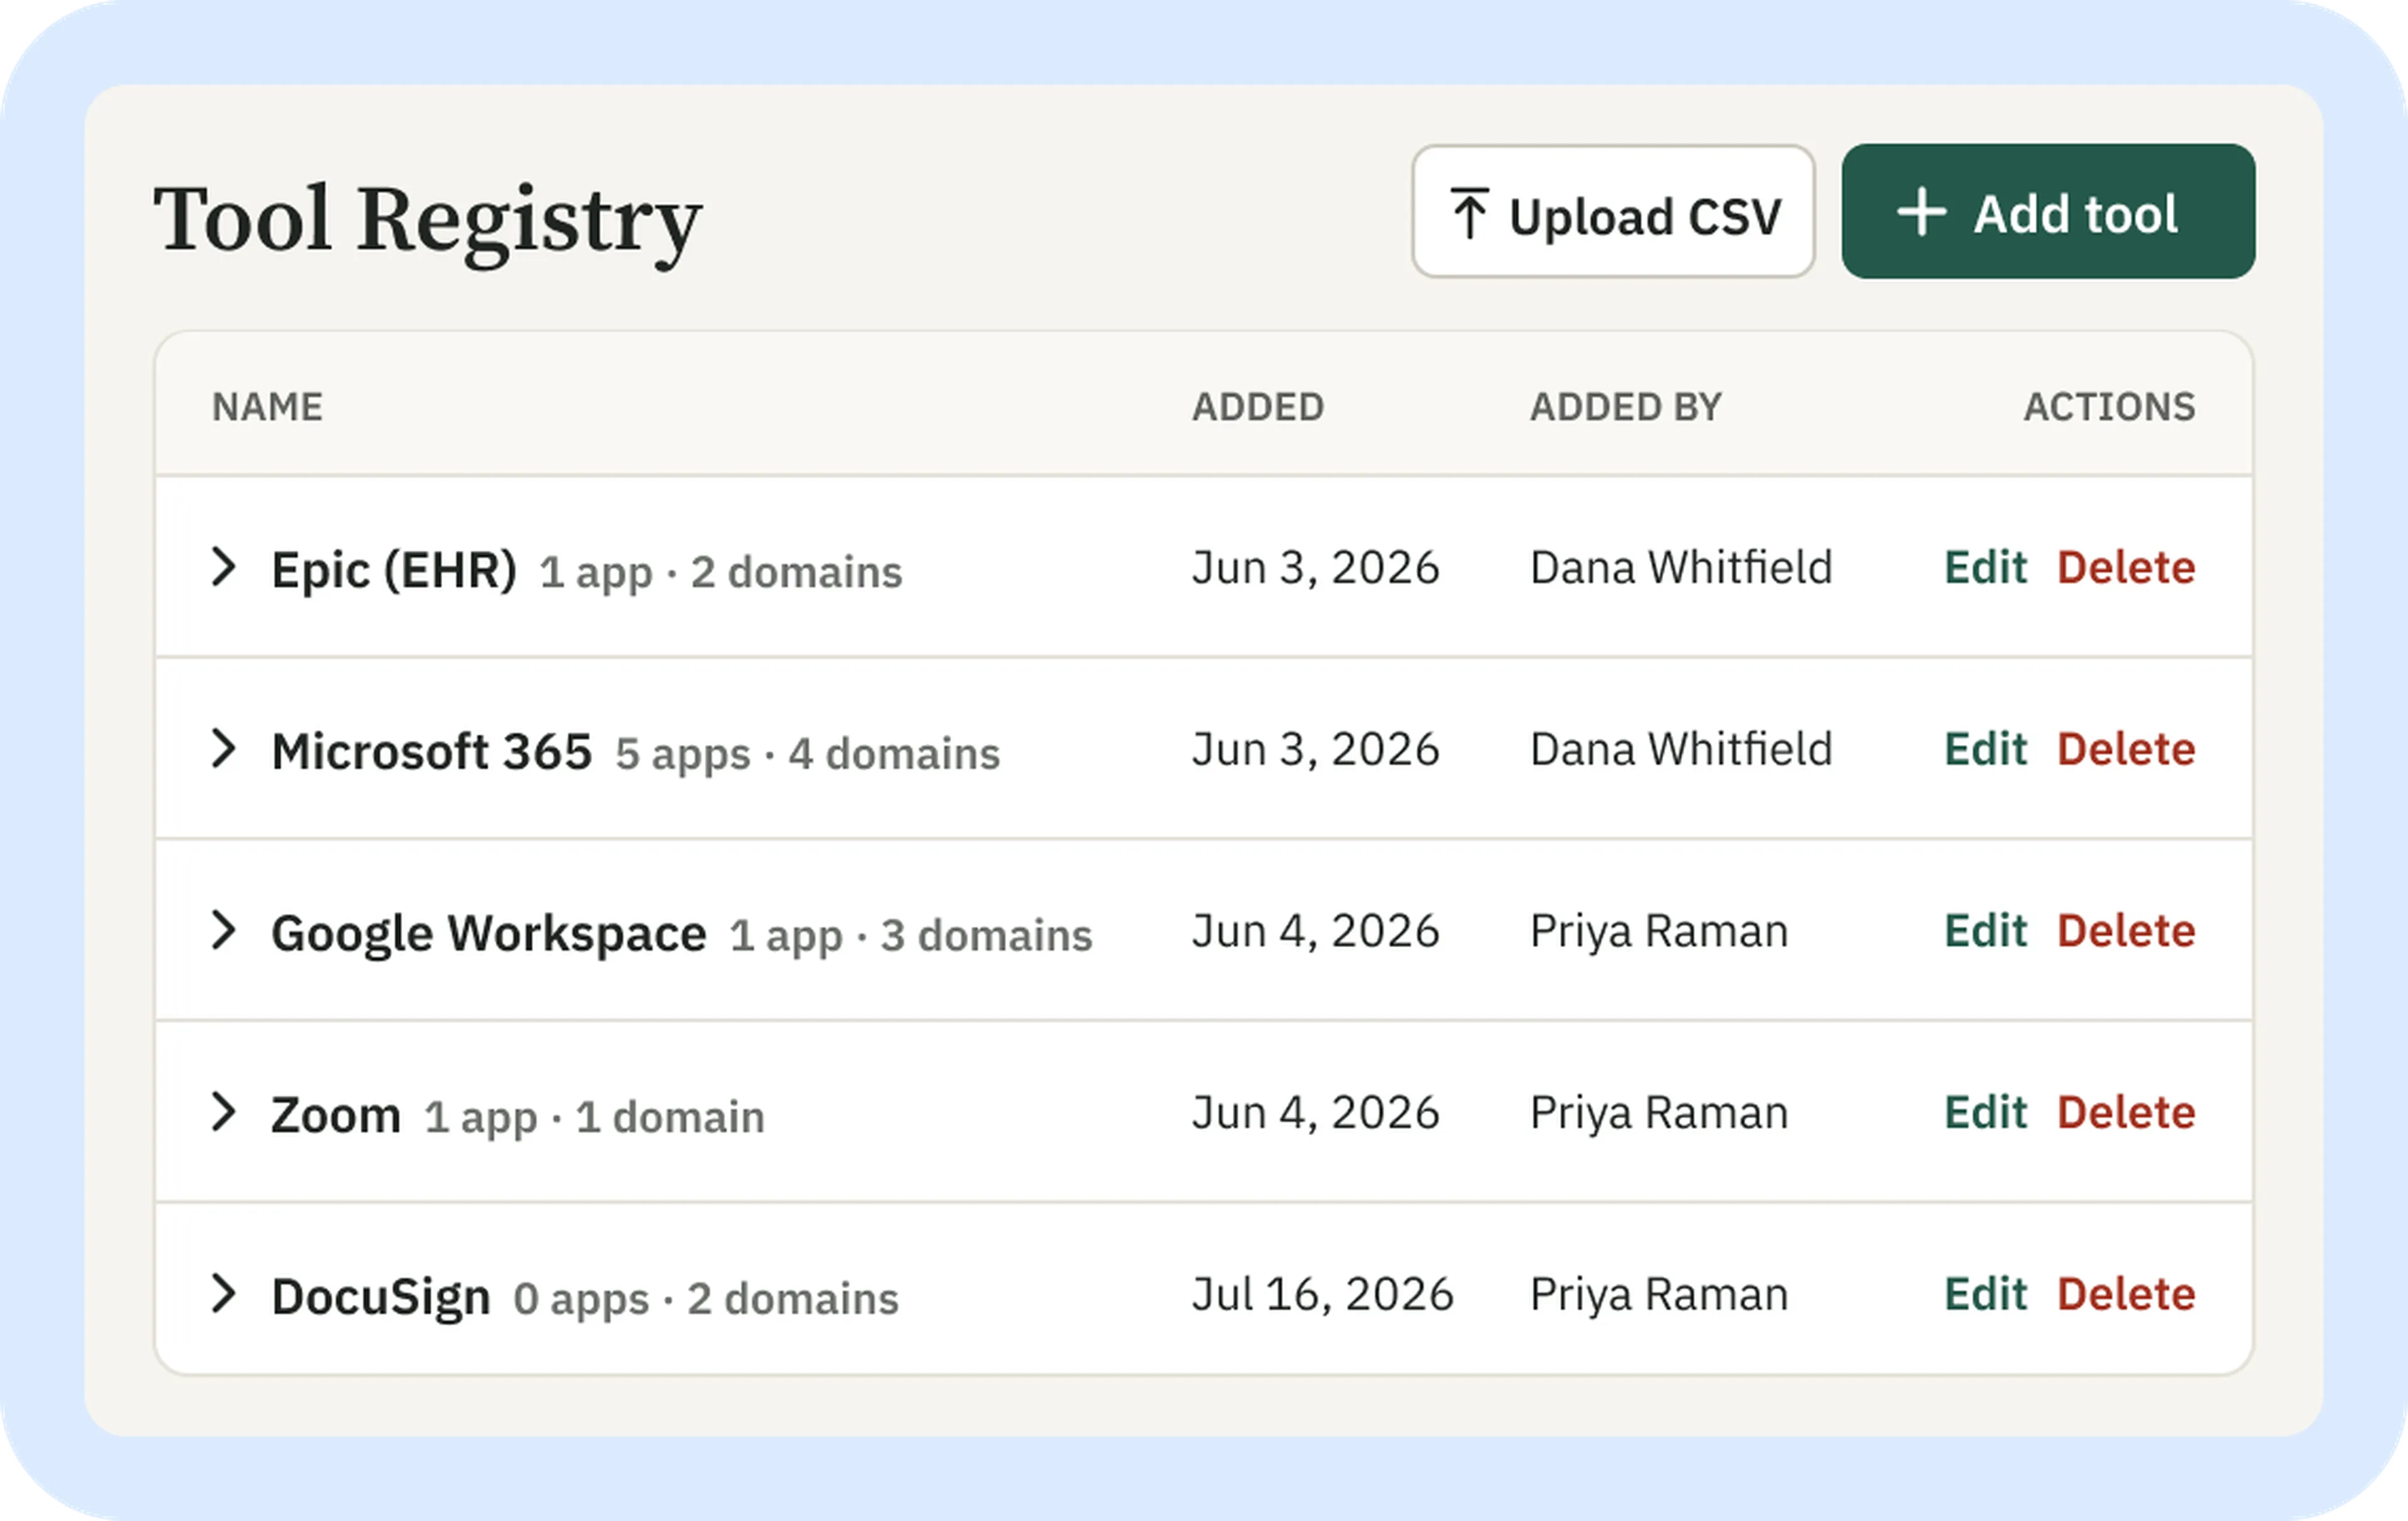
No written list of approved tools? Setting up Compliance Doctor gives you one.

Step 1

Detect

You set where patient data is allowed, such as your EHR and company email. Anything that moves somewhere else gets flagged.

Step 2

Decide

Each alert is ranked by severity and spells out what moved, where it went, the likely cause and a suggested next step. You make the call.

Step 3

Record

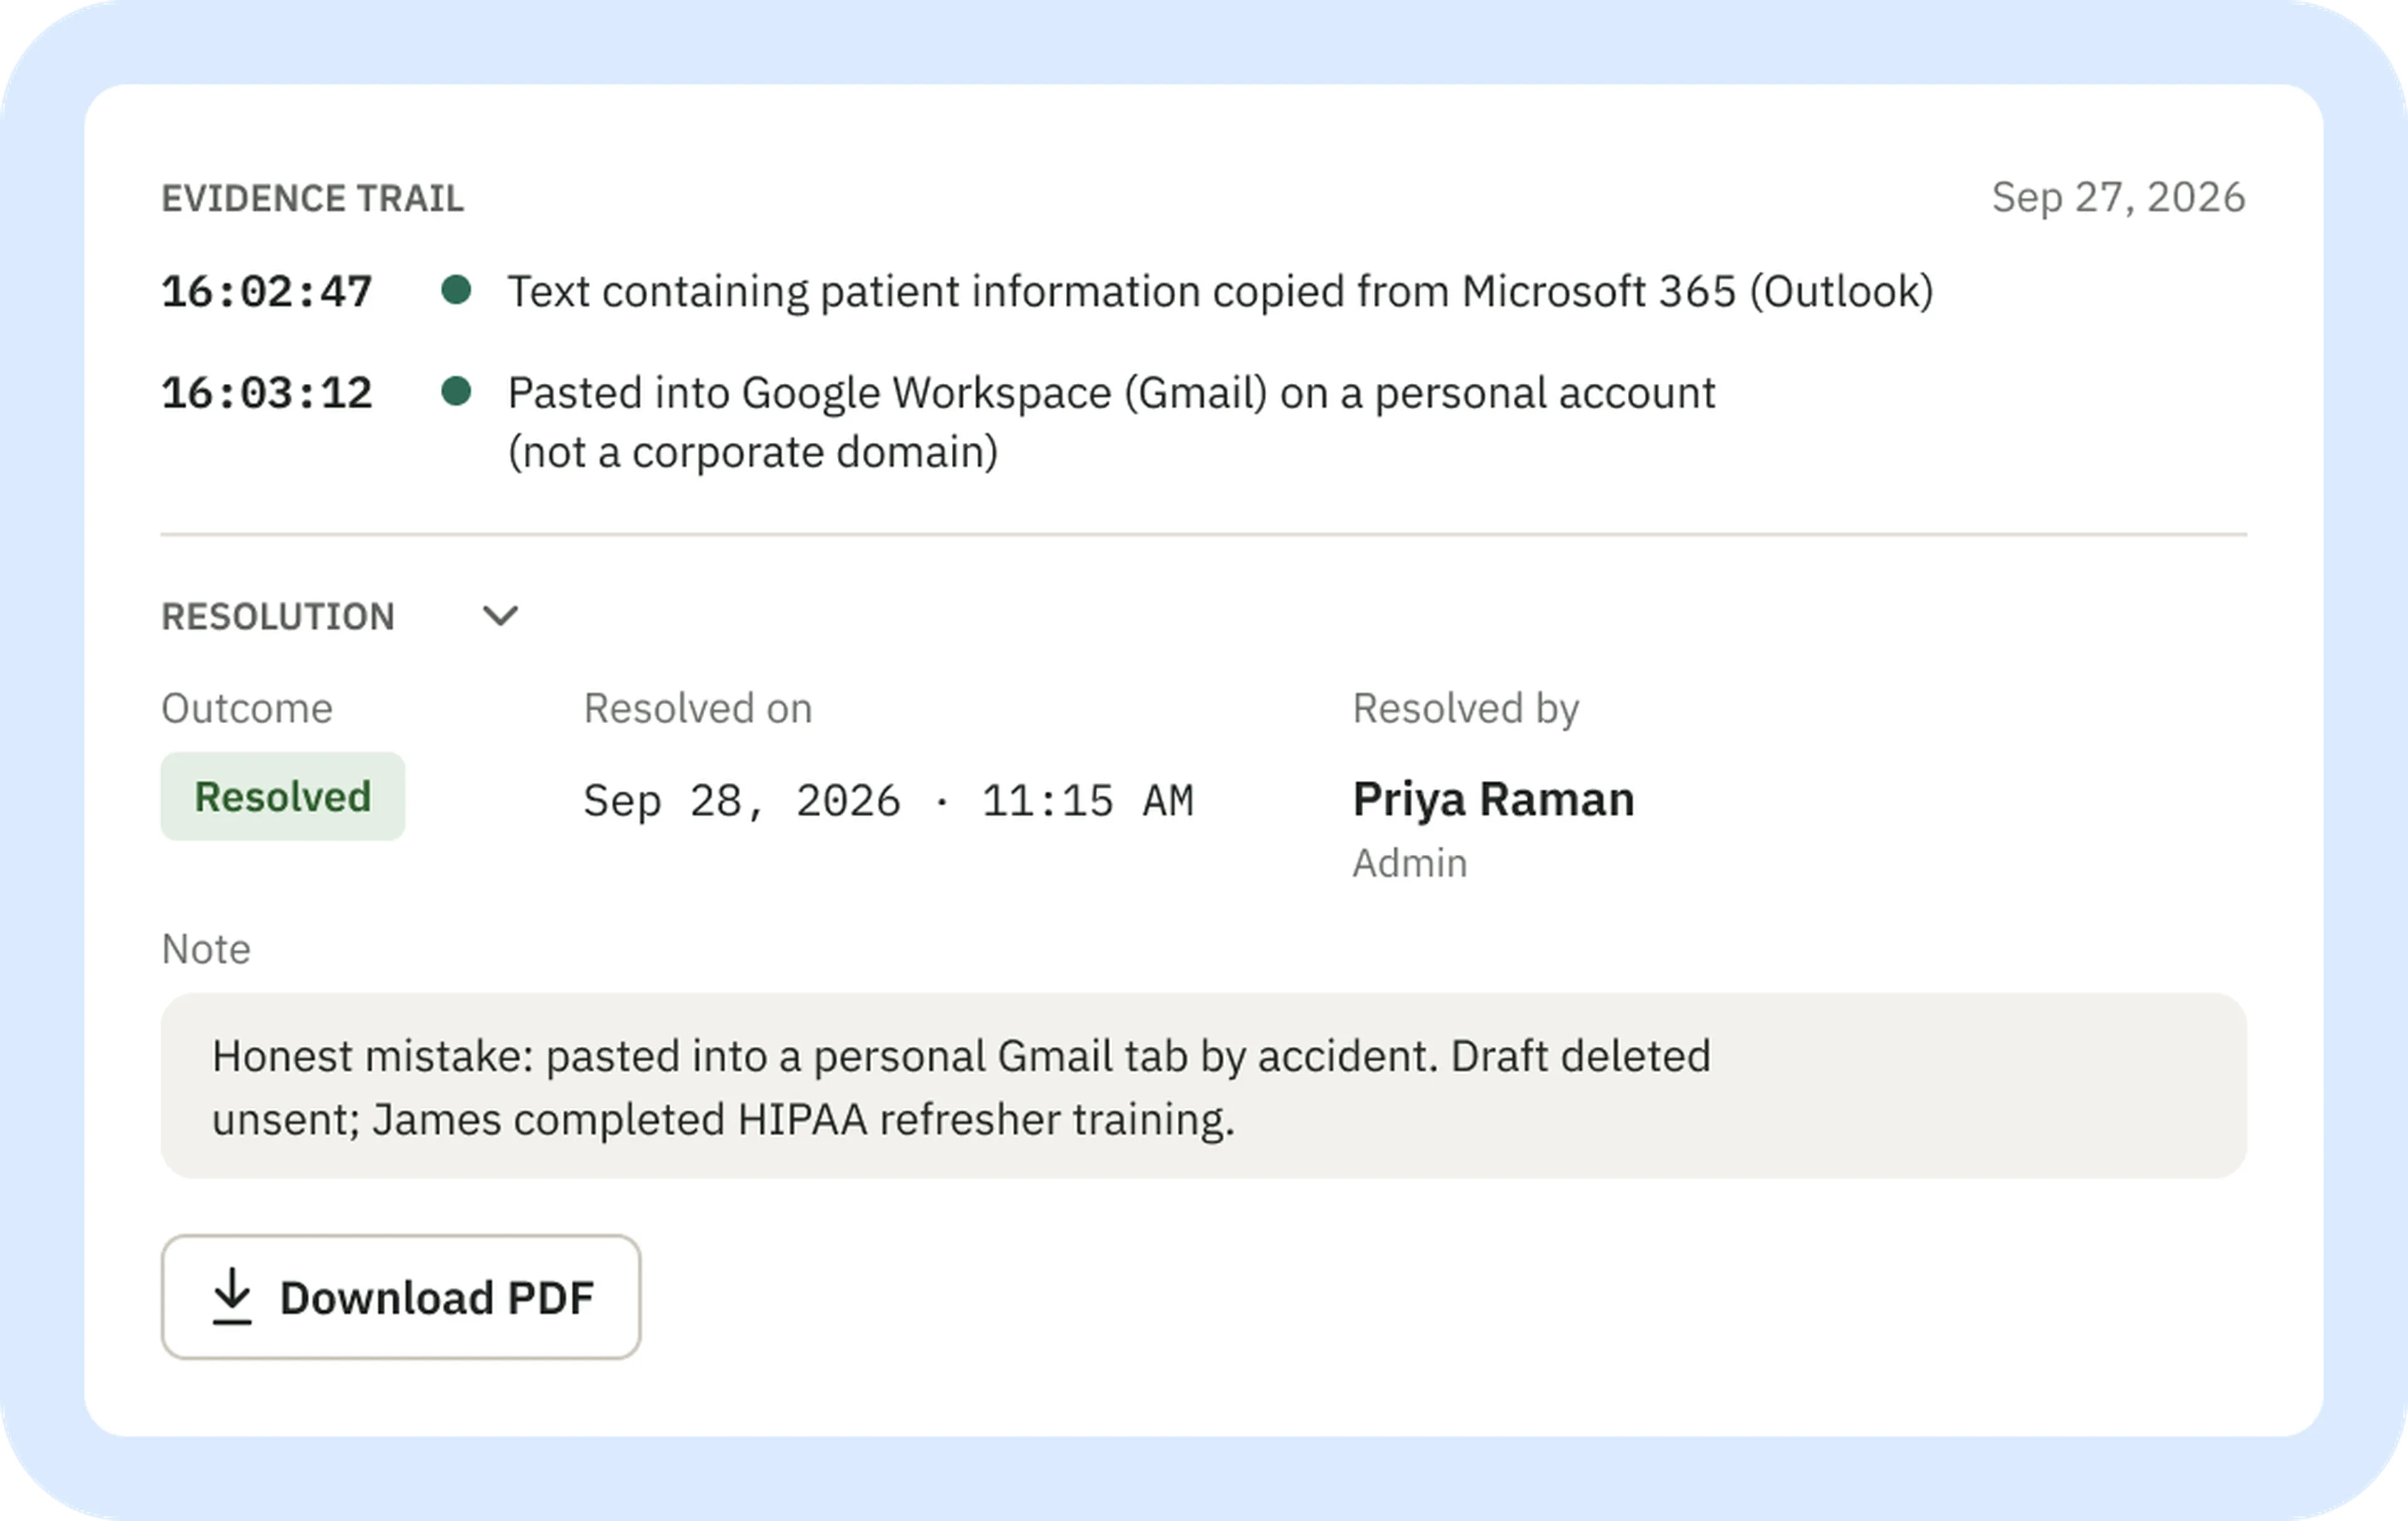
Your response is saved with its evidence trail, ready to export for leadership, clients or auditors.

Trust and security

Stays out of your team's way and keeps patient records where they are

Nothing is blocked

Staff keep their tools, and copy and paste still works.

Company account or personal?

Tells your company account apart from a staff member's personal one.

No new privacy problem

Patient records aren't stored, and PHI is never sent to an AI model.
RIGCERT ISO/IEC 27001:2022 certification
A-LIGN SOC 2 badge

Questions teams ask first

Get a demo

We'll flag a sample exposure and walk you through the alert, the decision and the evidence record, then check whether it fits how your team works.